📖 What Exactly Is a Threat?
I’ve sat in countless meetings where someone says “we’ve got a security threat” and half the room nods while picturing a shadowy figure in a hoodie, and the other half thinks of a dodgy email. Neither is completely wrong, but a threat in cybersecurity is far more specific — and worth wrapping your head around properly.
At its simplest, a threat is any potential cause of an unwanted incident that may result in harm to a system or organisation. Notice the word potential. A threat doesn’t mean the damage has happened yet; it’s the thing with the ability and the intent (sometimes natural or accidental) to cause you grief. Think of it as the “who” or “what” that could exploit a weakness.
🔍 Breaking It Down: The Anatomy of a Threat
A threat is not a single blob of badness. I find it useful to think of a threat as having a few moving parts:
🧍 Threat Actor (or Threat Agent)
The entity behind the threat. It could be a human (hacker, disgruntled employee), a group (organised crime, nation-state), or even non-human (a lightning strike, a faulty server that wipes data).
🎯 Threat Vector
The path or method used to deliver the malicious action. Email attachments, dodgy USB sticks, unpatched software, even physical intrusion all count.
⚡ Threat Event
The actual occurrence — a phishing email lands in an inbox, a storm floods a data centre, a brute-force login attempt begins.
Here’s the crucial nuance that many textbooks botch: a threat is not the same as an attack. The threat is the potential; the attack is the action. I might be threatened by a neighbour’s rickety tree overhanging my shed (the threat). The attack is when it actually falls during a storm.
🧭 Types of Threats (Because They’re Not All Hackers)
When I’m explaining threats to newcomers, I group them like this. It stops the “it’s all about malware” tunnel vision.
👤 Intentional Threats
- Malicious insiders: Someone within your organisation with an axe to grind or a payday from a competitor.
- Hacktivists: Driven by political or social causes, often defacing websites or leaking data.
- Cybercriminals: The name says it all — they want money, usually through ransomware, fraud, or selling stolen data.
- Nation-state actors: Advanced Persistent Threats (APTs) — incredibly patient, well-funded espionage or sabotage.
😵 Unintentional / Accidental Threats
- A well-meaning employee pasting sensitive data into the wrong chat window.
- A system admin misconfiguring a cloud storage bucket to public.
- Dropping a coffee on a critical server (yes, I’ve seen it).
🌪️ Environmental / Natural Threats
Floods, fires, earthquakes, power outages. These don’t have intent, but they absolutely can cause catastrophic damage.
The one thing I always stress: accidental threats are just as devastating as intentional ones. In fact, the 2023 Verizon Data Breach Investigations Report kept human error in the top causes of breaches. So don’t ignore the accidental bucket.
📬 Threat Vectors – The “How”
Understanding vectors makes a threat feel tangible. Here are the common delivery mechanisms:
- Phishing / spear-phishing emails – still the number one vector. A believable email tricks someone into handing over credentials.
- Compromised websites / drive-by downloads – just visiting a booby-trapped site infects you.
- Removable media – USB drops in car parks (curiosity kills the network).
- Software vulnerabilities – unpatched systems are an open door.
- Supply chain compromise – a threat actor slips malicious code into a trusted software update (think SolarWinds).
- Physical access – tailgating into an office, plugging a device directly.
🔗 Threat vs. Vulnerability vs. Risk
If you only remember one thing from this, let it be this distinction. I see seasoned professionals muddle these, so don’t worry if it takes a moment.
Threat: The “someone” or “something” that could do you harm. Example: a burglar.
Vulnerability: A weakness that can be exploited. Example: your back window doesn’t lock properly.
Risk: The likelihood and impact of a threat exploiting a vulnerability. Example: high risk because you live in a known burglary hotspot and that window is right next to an alley.
A threat without a vulnerability is often just noise. A vulnerability without a threat is a theoretical hole. Risk ties them together to help you prioritise.
🌐 Real-World Example: The Ransomware Threat
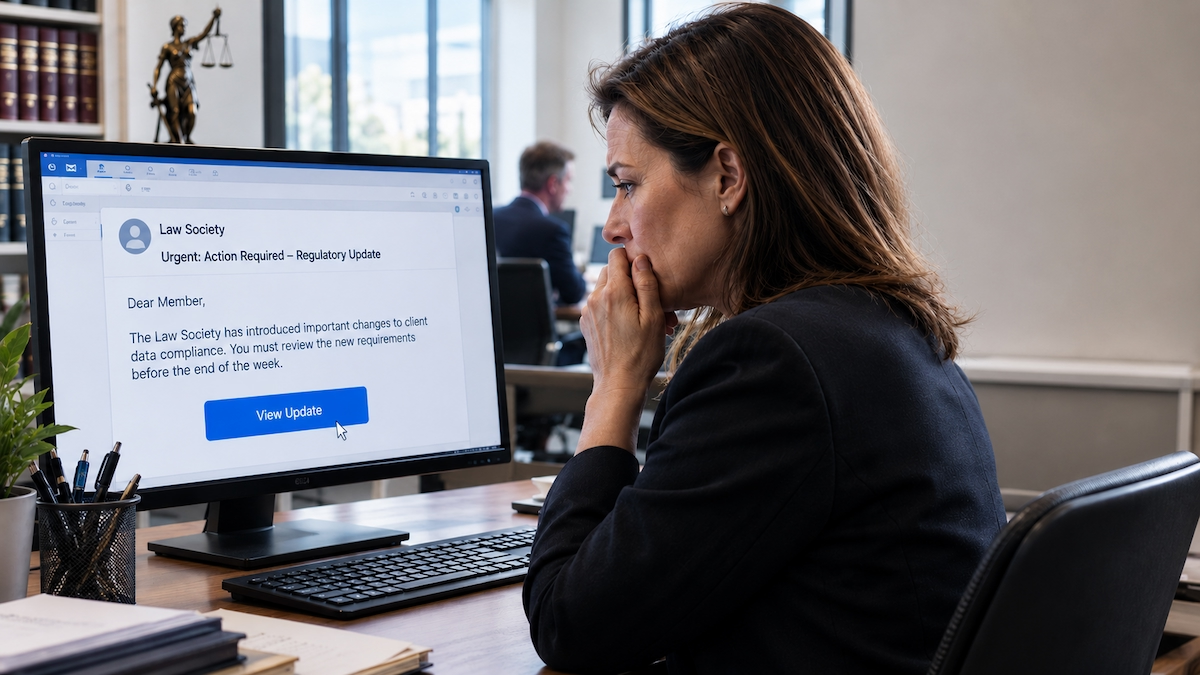
Let me ground this. Say you run a medium-sized legal firm. You have valuable client data, and your team uses email daily. A cybercriminal group (threat actor) wants money. They craft a convincing phishing email that looks like it’s from the Law Society (threat vector: email). The email lands in your office manager’s inbox. That’s a threat event — the potential is now active. If the manager clicks the link, the threat actor’s malware could encrypt your files (attack). Here, the threat was the criminal group and their malware campaign long before a single click happened. The vulnerability might be lack of security awareness training or an outdated email filter. The risk is the financial and reputational hit if those files are locked and sensitive cases are made public.
I’ve watched firms pay out tens of thousands because they didn’t separate the threat from the attack in their planning. Accept that threats are always present — it changes how you defend.
🔑 Key Points
- 🚨 A threat is a potential cause of harm — the “who” or “what” with the capacity and intent to do damage.
- 👤 Threat actors can be human (malicious, accidental) or non-human (natural disasters, failed hardware).
- 🛤️ Threat vectors describe the delivery path: email, USB, software flaw, physical access, etc.
- ⚡ A threat event is the moment that potential surfaces, not the actual damage itself.
- 🔗 Distinction matters: Threat exploits vulnerability, creating risk.
- 🎭 Intentional threats get the headlines, but accidental and environmental threats are equally destructive.
- 📈 Threats are constant — you don’t eliminate them, you manage the risk they pose.
❓ Knowledge Check
Here are three questions to test your understanding of the topic. Grab a cuppa and have a go.